When business operations stall and profits drop, software bloat and outdated hardware are often quietly to blame. Technology should accelerate your business, not create friction. Modernizing your tech strategy removes operational roadblocks, protects sensitive data, and helps your team stay focused on revenue-generating tasks.
IT Support Business Models by Macro Systems
Depending on simple push notifications or SMS codes to protect your organization's network is no longer sufficient. Today's hackers bypass these legacy multi-factor authentication methods through automated fatigue attacks and proxy phishing.
As a result, updating your authentication rules is essential to safeguard your team, clients, and data.
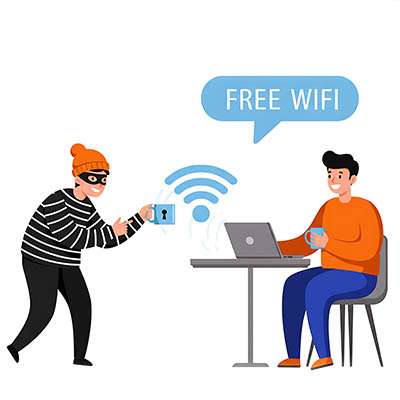
Imagine this: You’re settling into a cozy corner of your favorite local café. The aroma of roasted espresso fills the air, and you're ready to tackle your inbox. You pop open your laptop, connect to the local public hotspot, and dive into work.
The flexibility of working anytime and anywhere is incredibly tempting, but depending on free, public wireless networks can be exceptionally dangerous. While it might seem paranoid, it is easier than ever to stumble into a security nightmare when utilizing public Wi-Fi.
Gaining a competitive advantage rarely stems from flashy tricks or cutting corners. Outmaneuvering rivals requires sharp operational foresight, quiet reliability, and an infrastructure that eliminates daily friction. When your technology functions seamlessly and your assets remain secure, your organization moves faster than the rest.
Microsoft is ending support for SMS and voice multi-factor authentication in Entra ID, replacing them with phishing-resistant passkeys. Depending on phone codes already exposes your business to interception and SIM-swapping risks. Preparing your business now ensures uninterrupted sign-ins and protects your shared operational resilience.
Consider the heavy vaults of 19th-century London. A single key wouldn't open them so bankers engineered a "two-man rule" requiring two distinct keys held by two separate officers to turn the lock simultaneously. Builders knew that if a single lock or outer wall failed, a secondary barrier was the only thing standing between safety and total collapse.
Even so, fast-forward to today and many businesses are still depending on the electronic equivalent of a simple wooden latch: a lone password.
Phishing is a very popular form of cyberattack where hackers craft deceptive messages designed to trick you into revealing sensitive information or granting access to secure systems. Why is it so widespread?
Simple: breaking through sophisticated enterprise encryption is hard, and manipulating human psychology is significantly easier. That’s why phishing remains the single most common entry point cybercriminals use to compromise small and medium-sized business networks.
Getting your staff to adopt multi-factor authentication usually feels like pulling teeth. The pushback often happens because people see it as an irritating roadblock rather than a safety measure.
Fortunately, changing how your team views cybersecurity is far easier than you think, provided you drop the tech jargon and focus on real human impact.
When I explain the cloud to business owners, I usually tell them it's basically just entrusting a massive corporation to manage the computer for you. It's a great setup. You don't have to worry about physical server hardware catching fire, taking up space, or humming away in a dusty utility closet. Somewhere along the line, however, a major misunderstanding walked through the door.
A lot of people think that because their files live in the cloud, they are automatically backed up, safe, and completely off the hook. Believe me, it’s a nightmare when a business owner finds out the hard way that this isn’t true. Listed below is a look at what your cloud provider actually guarantees, and what they leave entirely up to you.
Artificial intelligence systems require massive amounts of information to operate effectively. When employees begin using these tools, the volume of data moving across a network increases rapidly. This surge creates operational challenges, security vulnerabilities, and system inaccuracies if it is not managed correctly from the start.
The marketing in the technology industry loves using complicated words for simple ideas, leaving normal business owners feel left behind. Looking past all the fancy sales pitches reveals that the Internet of Things is a practical concept; it just means putting an internet connection inside everyday equipment so those devices can send and receive useful updates.
This allows basic tools like your office thermostat, door locks, delivery trucks, and security cameras to talk over the internet. The main goal is simply getting helpful, quick updates sent straight to you to run things better.
If you analyze any modern corporate data breach, you’ll discover that it’s usually not a particularly complicated attack that breaks through. You’d think that intelligent, sophisticated business owners can spot simple attacks coming from a mile away, but the reality is that today’s threats don’t target a lack of intellect or knowledge, they go for the actual vulnerability in a busy executive’s workday: their cognitive bandwidth.
Without experience running a business, the intricacies of accepting credit card payments probably wouldn’t occur to the average person: there is a complex maze of requirements, rules, and standards that a business must meet before it may do so. These are what make up the Payment Card Industry Data Security Standard. Listed below: what these standards demand and what you need to do to ensure compliance is achieved… plus, why compliance is so imperative in the first place.
We’ve all seen the Hollywood version of a hacker: it’s usually a lone genius in a dark room, typing furiously into a glowing green screen, shouting "I'm in!" right before they bypass a mainframe.
It makes for great television. In the real world, however, this representation is completely wrong. Modern cybercriminals don't look like a movie villain. They look a lot more like a mid-level corporate executive.
Outfitting an entire team with brand-new smartphones and tablets is a massive expense. To save a bit of cash on equipment costs, a lot of small business owners choose a simpler path. They set up a Bring Your Own Device (BYOD) policy, allowing everyone to check company emails, look up client records, and jump into the corporate chat right from their personal phones.
It is convenient, but it also creates a massive data liability.
Most successful businesses don't succeed by being the first to invent a new way of doing things; they succeed by taking systems that already work and putting them to use for their particular needs. In the world of business technology, trying to be unique is usually a fast track to wasting money and facing technical headaches.
There was a time when Bring Your Own Device (BYOD) was seen as mutually beneficial. An employer could save significant costs by eliminating the need for new hardware investment, while the employee didn’t have to juggle devices and could stick with what was familiar and comfortable.
However, there is a significant drawback that could upend the undeniable usefulness of BYOD if it isn’t addressed: the inherent insecurity that the business needs to contend with.
Most business owners believe that more security naturally means less speed. They accept a clunky user experience because they think that’s the price of safety. However, this exposes a dangerous paradox: When security is too difficult to use, your team becomes less secure. If it takes ten minutes and three different devices to log in, your employee won’t work harder, they’ll work around you, taking productivity shortcuts that bypass your defenses entirely.